Projects & Publications

AI & Cybersecurity Projects & Research Artifacts

This section highlights my peer-reviewed research publications in AI and cybersecurity, focusing on practical security challenges informed by real-world systems and data. The work emphasizes problem formulation, empirical analysis, and validated insights, without exposing proprietary implementations.

What You’ll Find Here

  • Top-Tier Research Papers: Publications at leading venues such as ACM CCS, SIGMOD, SAC, and CoLLAs
  • AI for Cybersecurity: Studies on phishing detection, user behavior analytics, credential exposure, and threat intelligence
  • Privacy-Preserving & Federated Learning: Research addressing secure, communication-efficient, and non-IID distributed learning
  • Data Quality & Robust Evaluation: Analyses of annotation errors, label noise, and their impact on model reliability and security decisions
  • Industry-Informed Research: Problem settings motivated by large-scale, real-world security environments, abstracted to respect confidentiality

Each publication distills generalizable insights and lessons learned from applied research, contributing to both academic understanding and practical security decision-making.


Browse the publications below or use tags to explore specific research themes such as Federated Learning, Data Quality, Secure ML, and User Behavior Analytics
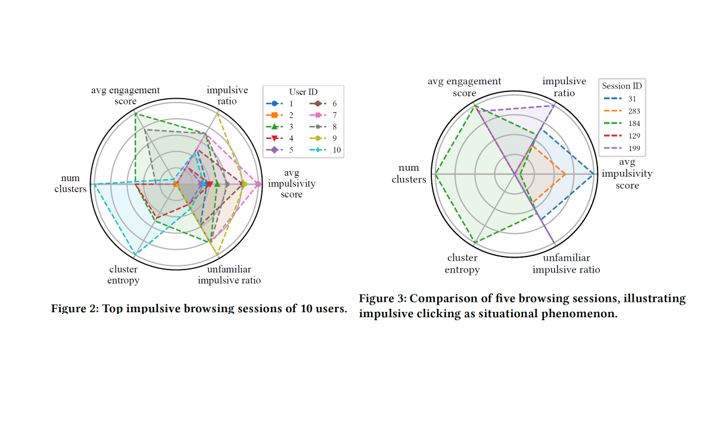
Impulse in the Clickstream -Behavioral Insights from Browsing History

Impulse in the Clickstream -Behavioral Insights from Browsing History

An empirical study of impulsive clicking behavior using real-world browser history data to enable adaptive, behavior-aware cybersecurity defenses.

cybersecurity user-behavior-analytics phishing browser-telemetry adaptive-security
Learn more
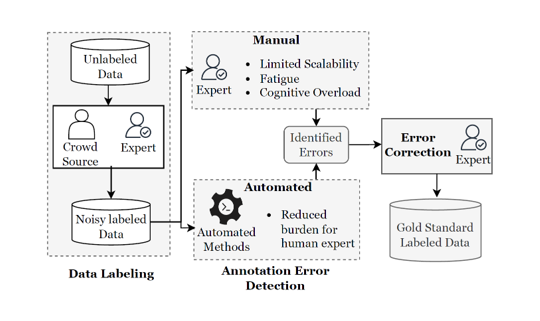
Toward Scalable Human-in-the-Loop Annotation Error Detection with Noise-Aware Training

Toward Scalable Human-in-the-Loop Annotation Error Detection with Noise-Aware Training

A systematic study of how label noise degrades annotation error detection systems and how simple noise-robust training strategies can restore scalability and reliability.

data-quality annotation-error-detection human-in-the-loop robust-ml label-noise data-centric-ai
Learn more
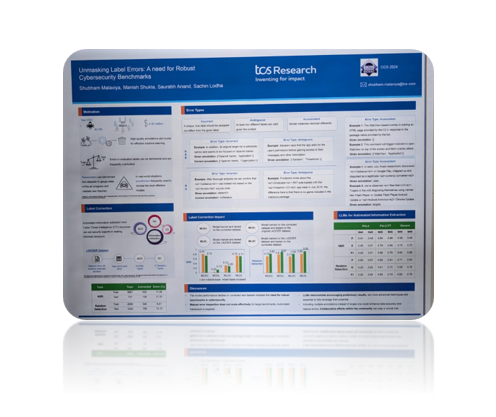
Unmasking Label Errors: Why Cybersecurity Benchmarks Need Stronger Benchmarks

Unmasking Label Errors: Why Cybersecurity Benchmarks Need Stronger Benchmarks

An empirical investigation into annotation errors in cybersecurity benchmarks, revealing how noisy test labels distort model evaluation and mislead progress in threat intelligence.

cybersecurity data-quality benchmarks threat-intelligence llms evaluation
Learn more
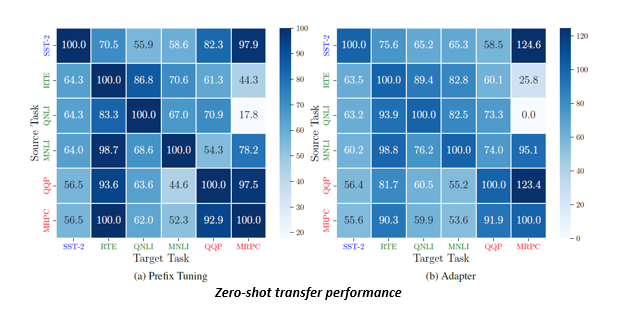
Reducing Communication Overhead in Federated Learning with Parameter-Efficient Finetuning

Reducing Communication Overhead in Federated Learning with Parameter-Efficient Finetuning

An empirical study showing how parameter-efficient finetuning enables scalable, privacy-preserving federated learning for large language models with drastically reduced communication costs.

federated-learning nlp parameter-efficient-tuning privacy distributed-ml transfer-learning
Learn more
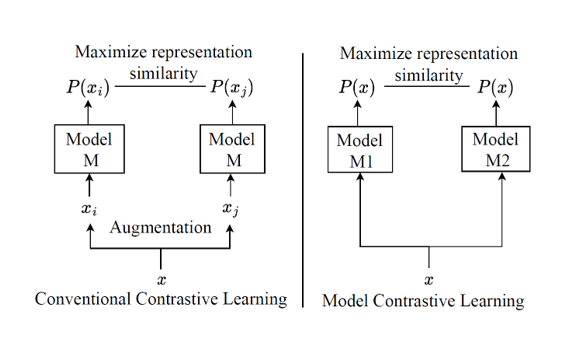
FedFAME: Rethinking Federated Semi-Supervised Learning Without Data Augmentation

FedFAME: Rethinking Federated Semi-Supervised Learning Without Data Augmentation

Introducing FedFAME, a data augmentation–free framework for federated semi-supervised learning that remains robust under extreme non-IID data distributions.

federated-learning semi-supervised-learning privacy non-iid-data contrastive-learning machine-learning-systems
Learn more
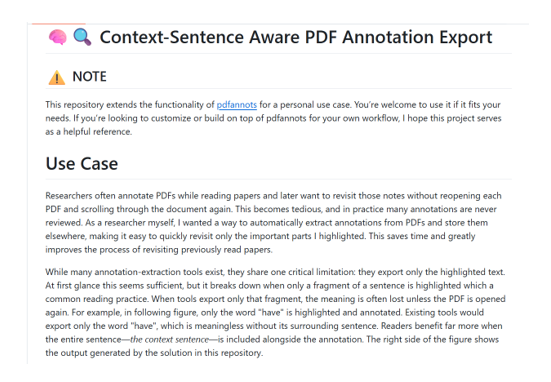
Context-Aware PDF Annotation Extraction for Research Productivity

Context-Aware PDF Annotation Extraction for Research Productivity

A practical utility to extract enriched context sentences for highlighted annotations in PDFs, augmenting standard annotation export tools with full-sentence context for better comprehension and reuse.

pdf annotation research-productivity data-extraction python academic-tools
Learn more